

2026’nın En İyi 10 Uyumluluk Takvimi Yazılımı

10 En İyi Uyumluluk Takvimi Yazılımı Kısa Listesi


Uyumluluk takvimi yazılımı, işletmeniz genelindeki mevzuata ilişkin son tarihleri ve uyumluluk görevlerini düzenlemenize, izlemenize ve yönetmenize yardımcı olur. En iyi uyumluluk takvimi yazılımını arıyorsanız, son tarih stresini azaltmanın, gereklilikleri merkezileştirmenin ve denetim hazırlığını iyileştirmenin yollarını arıyorsunuz demektir. Mevzuata ilişkin bir bildirimin veya politika incelemesinin kaçırılması, işletme açısından ciddi sonuçlar doğurabilir; bu nedenle doğru platformu seçmek önemlidir.
Bu rehber, karmaşık gereklilikler üzerinde görünürlük ve kontrol sahibi olması gereken proje yöneticileri, risk liderleri ve departmanlar arası ekipler için tasarlanmış en iyi araçlara odaklanır. İş akışınıza ve zaman çizelgelerinize uyan, iş birliğini destekleyen ve maliyetli gözden kaçırmaları önlemenize yardımcı olan uyumluluk çözümlerini bulmak için okumaya devam edin.
Why Trust Our Software Recommendations
Our team has been testing and reviewing software since 2012. As project managers ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria. We also draw on insights from industry thought leaders and practicing project management experts.
Our reviews reflect our human editorial judgment, not a sales pitch.
Expert reviewers:
Uyumluluk Takvimi Yazılımı Karşılaştırma Tablosu
Bu karşılaştırma tablosu, en iyi uyumluluk takvimi yazılımı seçimlerim için fiyatlandırma ayrıntılarını özetlemektedir:
| Tool | Starting Price | Website | |
|---|---|---|---|
| Best for collaborative compliance documentation | 4.6 out of 5 | Pricing upon request Free demo available | Website |
| Best for workflow automation at scale | 4.4 out of 5 | Pricing upon request Free demo available | Website |
| Best for audit-ready compliance reporting | 4.4 out of 5 | Pricing upon request Free demo available | Website |
| Best for scalable enterprise compliance programs | 3.3 out of 5 | Pricing upon request Free demo available | Website |
| Best for proactive regulatory change alerts | — | Pricing upon request Free demo available | Website |
| Best for real-time task evidence collection | 4.6 out of 5 | Pricing upon request Free demo available | Website |
| Best for customizable workflow automation | 4.6 out of 5 | Pricing upon request Free demo available | Website |
| Best for tech stack integration flexibility | 4.4 out of 5 | Pricing upon request Free demo available | Website |
| Best for integrated expert compliance guidance | — | Pricing upon request Free demo available | Website |
| Best for AI-driven compliance automation | — | Pricing upon request Free demo available | Website |
En İyi Uyumluluk Takvimi Yazılımı İncelemeleri
Aşağıda, kısa listeme giren en iyi uyumluluk takvimi yazılımlarının ayrıntılı özetlerini bulabilirsiniz. İncelemelerim, size en uygun olanı bulmanıza yardımcı olmak için her platformun özelliklerine, en iyi kullanım alanlarına ve entegrasyonlarına ayrıntılı bir bakış sunmaktadır.
Workiva
Best for collaborative compliance documentation
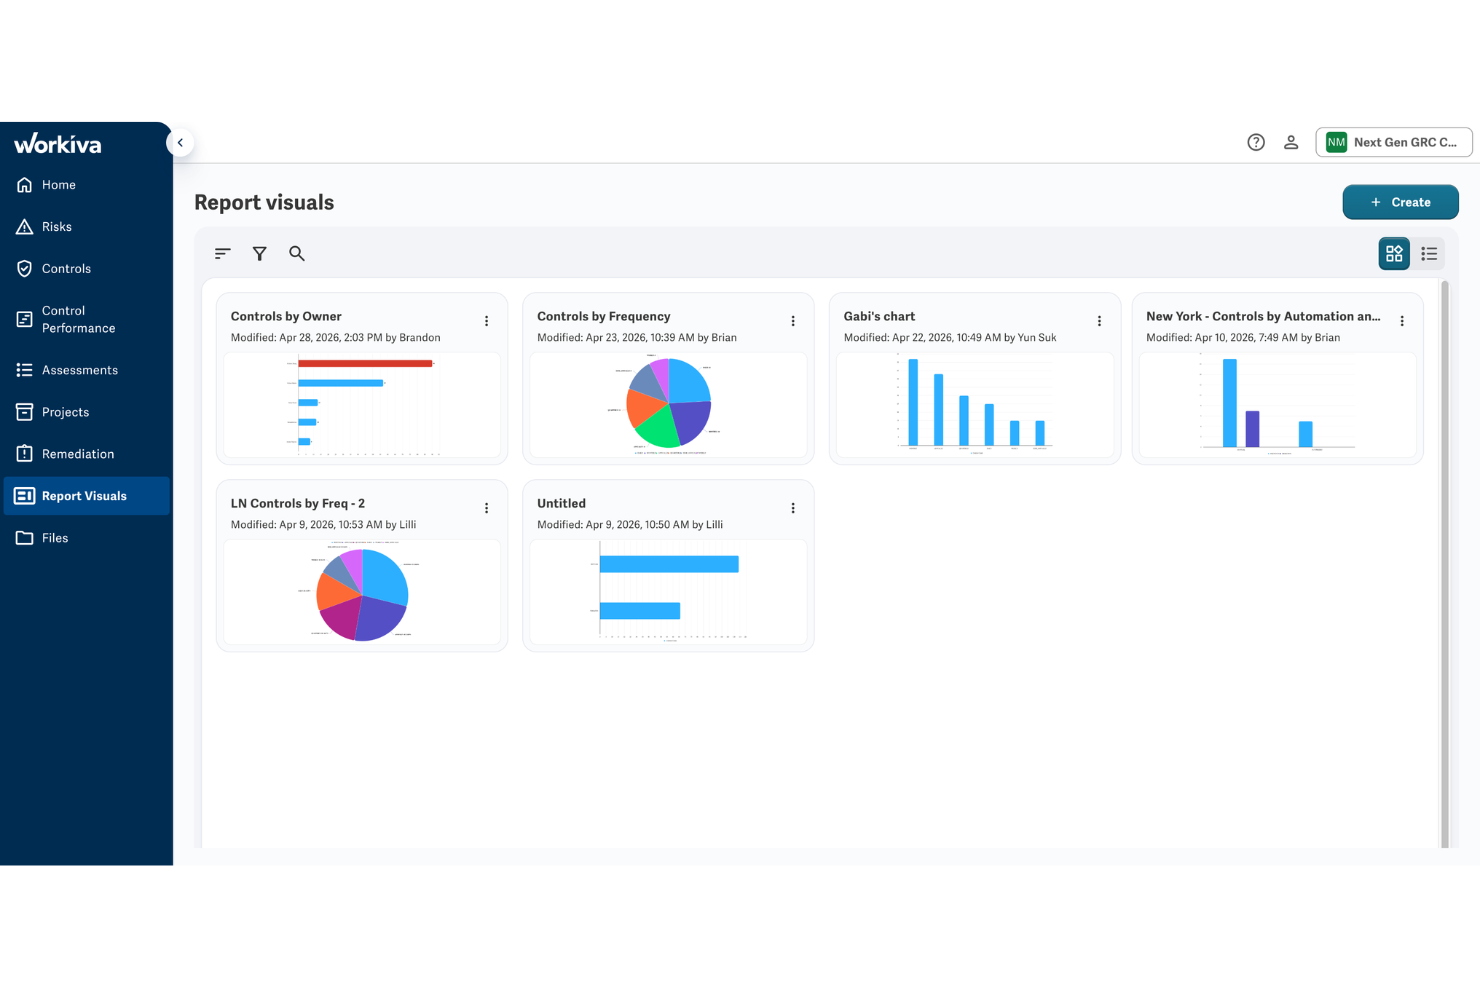
Workiva is a GRC platform that connects internal audit, risk management, controls testing, and compliance documentation inside a single connected workspace for enterprise teams.
Who Is Workiva Best For?
Workiva is a strong fit for compliance and internal audit teams at publicly traded or heavily regulated enterprises.
Why I Picked Workiva
Workiva earns its spot on my shortlist because the real-time co-authoring feature lets multiple compliance owners edit the same policy or control document simultaneously, without version conflicts. I also like that linked data means updating a control description in one place cascades across every connected report and framework mapping automatically. In practice, my team avoids the back-and-forth of emailing document drafts across stakeholders entirely.
Workiva Key Features
- Compliance framework mapping: Map controls directly to frameworks like SOX, COSO ERM, and CMMC 2.0 within the platform
- Risk assessment tools: Score and prioritize risks using built-in assessment templates tied to your control environment
- Audit management workflows: Manage audit scoping, fieldwork, and reporting inside structured project workflows
- Compliance dashboards: View control status, open issues, and remediation progress across the full compliance program
Workiva Integrations
Workiva connects to on-premises and cloud applications through its Wdata connectors, including Google Sheets, Microsoft Excel, Microsoft SharePoint, Oracle EPM, Salesforce, and SFTP, while premium connectors cover SAP, NetSuite, Workday, Snowflake, Power BI, ServiceNow, Anaplan, and many Oracle products. An API is available for custom integrations.
Pros and Cons
Pros:
- Built-in AI flags control coverage gaps
- Linked data auto-updates across all reports
- Real-time multi-user document co-authoring
Cons:
- Primarily built for enterprise-scale organizations
- Setup and onboarding require significant resources

Best for workflow automation at scale

Built on the Now Platform, ServiceNow GRC is an enterprise compliance and risk management platform covering integrated risk management, continuous compliance monitoring, third-party risk, business continuity, and privacy management.
Who Is ServiceNow Best For?
ServiceNow GRC is well suited to global enterprises that already run IT operations on the Now Platform and want compliance and risk management embedded in the same environment.
Why I Picked ServiceNow
I've included ServiceNow on this list because no other platform matches its ability to automate compliance workflows at enterprise scale. Its Integrated Risk Management module lets you map controls to obligations and trigger automated evidence collection tasks, so recurring deadlines don't depend on someone remembering to chase them. I also like that continuous compliance monitoring runs in real time on the Now Platform, flagging control failures and routing remediation tasks automatically without a manual review cycle in between.
ServiceNow Key Features
- Pre-built regulatory content library: Access pre-mapped control frameworks for standards like ISO 27001, SOC 2, and NIST out of the box.
- Issue and exception management: Log compliance exceptions, assign owners, set due dates, and track resolution status in a structured workflow.
- Attestation management: Collect and record stakeholder sign-offs on control performance at scheduled intervals.
- Performance analytics dashboards: View real-time metrics on control health, open issues, and compliance posture across business units.
ServiceNow Integrations
Native integrations are not publicly listed. An API is available for custom integrations.
Pros and Cons
Pros:
- Now Assist AI cuts repetitive GRC work
- CMDB links risks to specific IT assets
- Change tickets auto-generate compliance evidence
Cons:
- Fewer pre-built compliance frameworks than competitors
- Limited value without broader ServiceNow adoption

Resolver
Best for audit-ready compliance reporting

Resolver is a GRC platform that centralizes regulatory obligations, controls, policies, compliance testing, and audit evidence, with AI-assisted workflows for regulatory change tracking and audit preparation.
Who Is Resolver Best For?
Resolver is a strong fit for organizations in heavily regulated industries, like financial services or healthcare, where audit cycles are frequent and evidence requirements are strict.
Why I Picked Resolver
Resolver earns its spot on my shortlist because its regulatory obligation mapping connects specific rules directly to the controls built to address them, so nothing falls through during an audit. I also like how control testing workflows schedule and log each testing activity, giving auditors a clear record of what was tested, when, and by whom. When gaps appear, the issue tracking feature assigns owners and monitors fixes, so nothing sits unresolved.
Resolver Key Features
- Regulatory change tracking: Monitors updates to relevant regulations and routes changes into review workflows for assessment.
- Evidence repository: Stores and organizes compliance evidence, linked directly to the controls and audits it supports.
- Board-ready dashboards: Displays compliance status by framework, risk area, or region in a filterable visual format.
- Policy review scheduling: Tracks policy review cycles and sends automated reminders when reviews are due.
Resolver Integrations
Native integrations are not publicly listed. An API is available for custom integrations.
Pros and Cons
Pros:
- Tracks multi-region compliance in one platform
- AI drafts controls from the regulatory context
- Maps obligations directly to controls automatically
Cons:
- Narrow third-party integration options available
- Initial setup and configuration are time-consuming

Best for scalable enterprise compliance programs

MetricStream is an enterprise GRC platform with a dedicated compliance management product that centralizes regulatory obligations, certificate renewals, policy management, control testing, risk assessments, and incident tracking across large organizations.
Who Is MetricStream Best For?
MetricStream is a strong fit for compliance officers and risk teams at large enterprises managing complex, multi-framework regulatory programs across multiple business units.
Why I Picked MetricStream
I've included MetricStream on my shortlist because it's one of the few compliance platforms built to scale across large, multi-entity organizations without losing structural integrity. I like how the Compliance Environment and Process Design feature lets you map regulations, risks, controls, and policies into a single hierarchy across business units and locations. The Regulatory Intelligence capability automatically maps incoming regulatory updates to existing controls and policies, so my team isn't manually chasing changes across frameworks.
MetricStream Key Features
- Enhanced control testing: Design control tests and self-assessments as surveys or questionnaires, assign samples to control owners, and upload results in bulk via Excel or individually.
- Intelligent issue and action management: Uses AI/ML to automatically identify duplicate issues and recommend issue classifications and action plans.
- Compliance certifications: Lets business unit heads submit certifications and sub-certifications confirming their departments have addressed specific control concerns.
- Regulatory engagement management: Tracks examinations, regulator meetings, and information requests through automated workflows, with centralized storage of findings and action plans.
MetricStream Integrations
MetricStream offers marketplace integrations with BitSight, BMC, Cube, Dow Jones, Dun & Bradstreet, Jira, Qualys, Rapid7, ServiceNow, and Tenable. It also supports REST and Kafka-based connectors with 200+ built-in GRC APIs for custom integrations.
Pros and Cons
Pros:
- Centralized regulatory change tracking workflows
- Modular setup across risk and compliance
- AI flags duplicate issues automatically
Cons:
- Navigation buries tasks under layered menus
- Custom reports often need vendor support

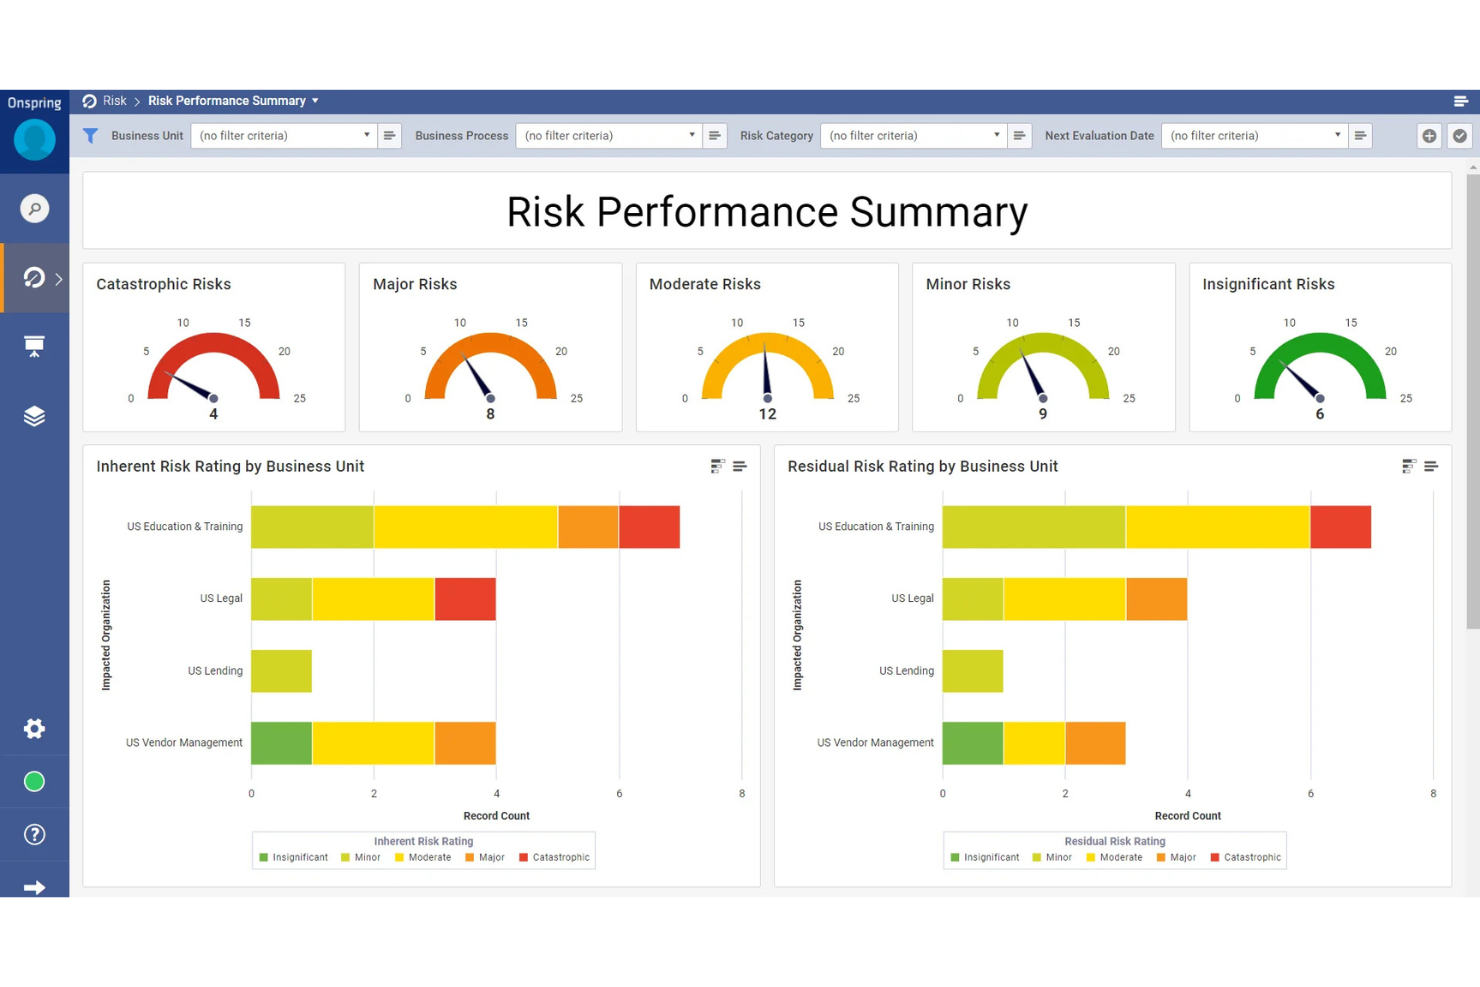
Onspring is a regulatory change management platform that maps incoming regulatory updates to controls, policies, and procedures, with AI-assisted impact assessments, automated review workflows, and one-click compliance reporting.
Who Is Onspring Best For?
Onspring suits mid-to-large enterprises with dedicated compliance teams who need to monitor, assign, and close out regulatory changes across multiple business units or frameworks.
Why I Picked Onspring
Onspring earns its spot on my shortlist because its horizon scanning pulls regulatory updates from global and local sources before changes take effect. I like that every incoming rule gets mapped directly to affected controls and procedures inside the rules register, so my team immediately knows what needs updating. The proactive alert system flags upcoming changes before deadlines arrive, keeping the compliance calendar accurate without relying on manual monitoring.
Onspring Key Features
- AI-assisted impact assessment: Automatically scores incoming regulatory changes and recommends the right analyst for triage and review.
- Multi-level review workflows: Routes change tasks through sequential approval stages with automated notifications at each step.
- Audit trail logging: Records every action taken on a regulatory change from initial alert through final sign-off.
- Compliance dashboard: Displays real-time status across all active regulatory changes in a single view.
Onspring Integrations
Onspring integrates with Jira, DocuSign, OneDrive, Google Drive, Microsoft Entra ID, Slack, Microsoft 365, and Azure DevOps, and an API is available for custom integrations.
Pros and Cons
Pros:
- Real-time rule change alerts from regulators
- AI matches regulatory controls across frameworks
- Drag-and-drop compliance workflow creation without coding
Cons:
- No sandbox environment for testing configurations
- Reporting visuals feel clunky to customize

Best for real-time task evidence collection
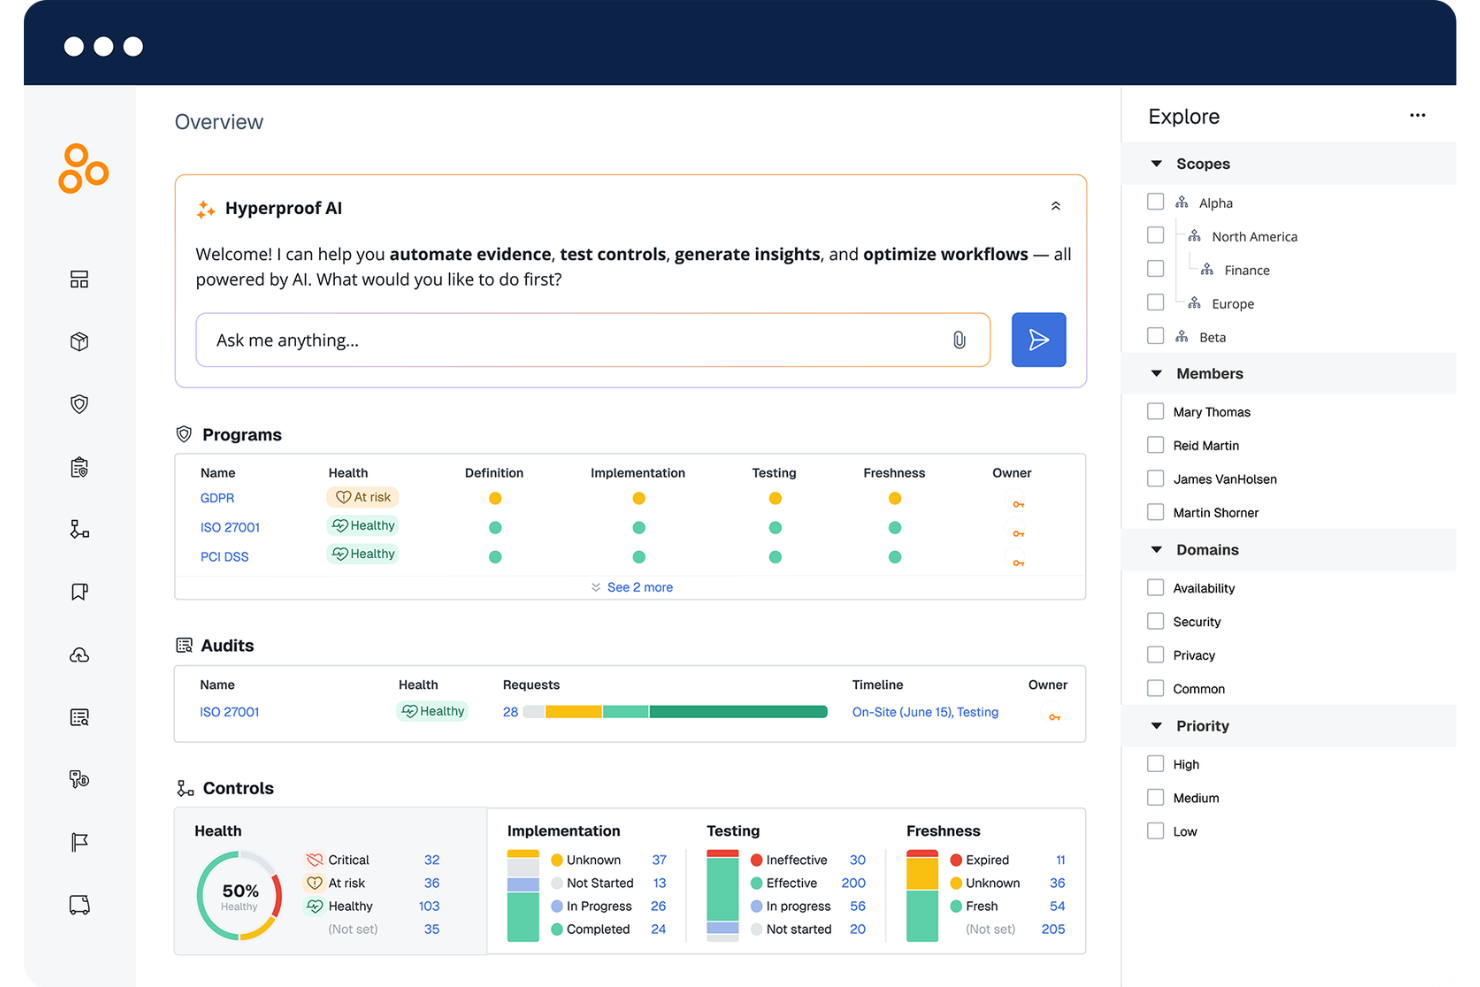
Hyperproof is an AI-powered compliance and task management platform that centralizes control mapping, evidence collection, audit preparation, and policy version management across multiple frameworks.
Who Is Hyperproof Best For?
Hyperproof is a strong fit for compliance, security, and risk teams at mid-size to enterprise companies managing multiple overlapping regulatory frameworks.
Why I Picked Hyperproof
Hyperproof is one of my top picks because I love how it handles real-time evidence collection at the task level. When my team assigns a control owner, Hyperproof auto-creates tasks based on test status and can automatically pull in evidence without waiting for manual uploads. I also rely on the audit dashboard to see exactly which requests are pending, in progress, or complete, so nothing slips through during crunch time.
Hyperproof Key Features
- Cross-framework control mapping: Map and reuse a shared set of controls across multiple compliance frameworks to reduce duplicate work.
- Policy version management: Create, store, and manage organizational policies in one centralized location with built-in version control.
- User access reviews: Adjust and verify user permissions in real time, with visibility into review status across your organization.
- Auditor collaboration workspace: Invite external auditors into a dedicated audit space where they can access only the information relevant to their review.
Hyperproof Integrations
Hyperproof offers native integrations with AWS, Azure, Google Drive, SharePoint, Dropbox, Amazon S3, Confluence, Jira, Asana, ServiceNow, and more. It also provides a Hypersync API for building custom integrations.
Pros and Cons
Pros:
- Built-in audit dashboard tracks request status
- Automated Hypersyncs collect evidence without manual uploads
- Reuses evidence across multiple compliance frameworks
Cons:
- Navigation gets difficult with large control lists
- Dashboards and analytics lack advanced customization

Best for customizable workflow automation
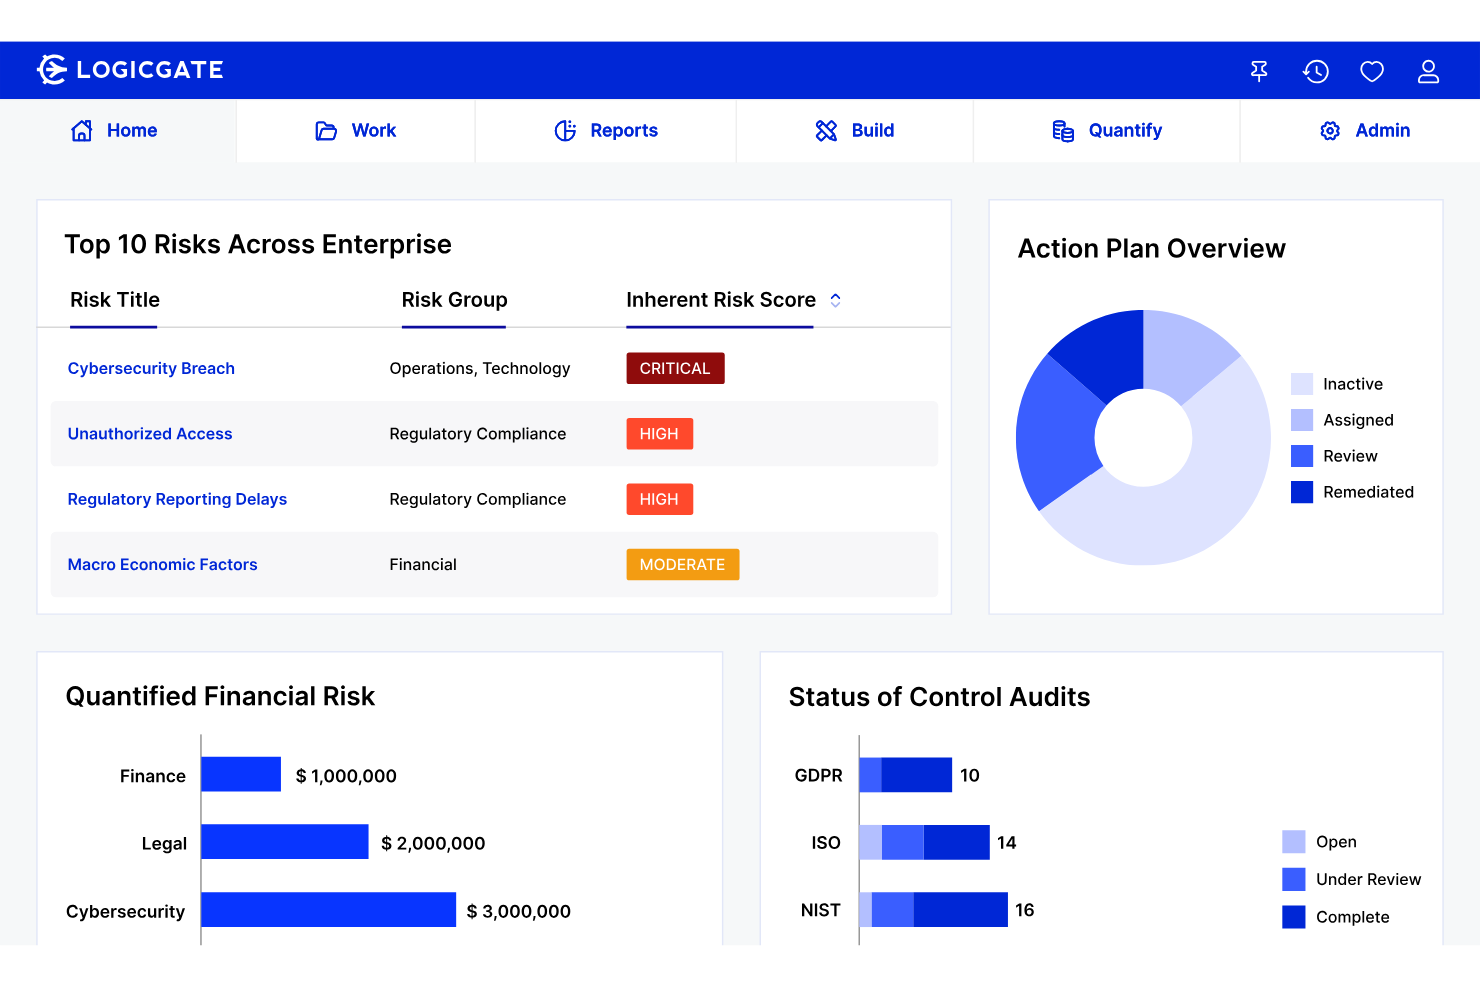
LogicGate Risk Cloud is a GRC platform that centralizes compliance management, audit workflow automation, multi-framework control mapping, and regulatory tracking across your organization.
Who Is LogicGate Best For?
LogicGate is a strong fit for compliance and audit teams at mid-to-large enterprises that need to build and customize their own GRC workflows without relying on vendor configuration.
Why I Picked LogicGate
I've included LogicGate in my top picks because its no-code workflow builder gives my team direct control over how compliance processes are designed and triggered. Instead of working around a vendor's fixed audit templates, I can build custom remediation workflows that route findings to the right owner automatically. I also use its regulatory compliance module to link obligations directly to assessments and findings, so nothing falls through the cracks between scheduled reviews.
LogicGate Key Features
- Multi-framework control mapping: Map and manage compliance across frameworks like SOC 2, ISO 27001, and NIST from a single unified view.
- Automated evidence collection: Automatically gather and organize audit evidence to reduce manual collection effort across assessments.
- Internal audit management: Plan, track, and close internal audits with built-in tools for due diligence, evidence gathering, and stakeholder reporting.
- Data privacy workflow management: Track personal data usage, handle data subject requests, and automate responses to maintain consistent privacy compliance.
LogicGate Integrations
LogicGate offers 200+ native integrations, including Jira, Slack, Microsoft 365, UKG, Snowflake, Asana, HubSpot, Hive, Power BI, and Zendesk. An open RESTful API is available for custom integrations.
Pros and Cons
Pros:
- Adapts workflows to any regulatory framework
- Links cross-module audit and risk data
- No-code workflow builder needs zero coding
Cons:
- AI capabilities trail behind competing GRC tools
- Advanced reporting needs heavy custom configuration

OneTrust
Best for tech stack integration flexibility
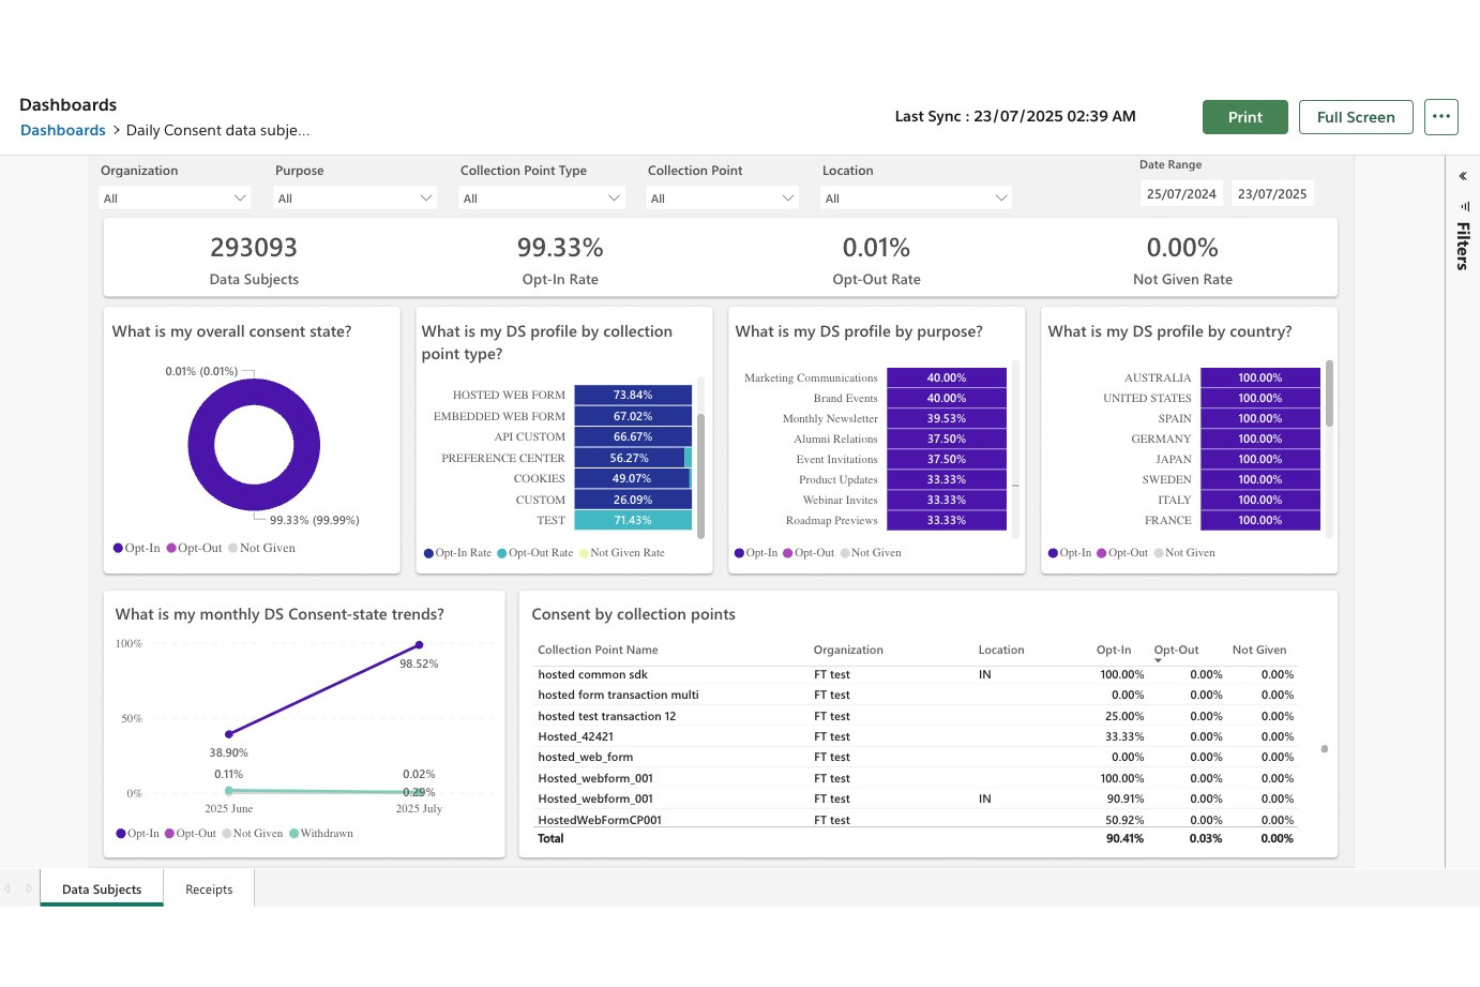
OneTrust is a GRC platform built for IT and security teams that combines compliance automation, IT risk management, policy tracking, and control monitoring across 55+ frameworks.
Who Is OneTrust Best For?
OneTrust fits enterprise security and compliance teams that need to manage IT risk across interconnected systems and multiple regulatory frameworks simultaneously.
Why I Picked OneTrust
I picked OneTrust as one of the best because of how well it connects compliance work to the tools your team already uses. The integrations gallery includes 500+ pre-built system connectors, and you can build new ones with a visual builder that doesn't need IT involvement. I also like that it uses pre-architected collectors to pull evidence directly from your tech stack, which cuts out a lot of manual work when you're tracking controls across multiple systems.
OneTrust Key Features
- Scoping survey: Run an initial survey to define your compliance scope and surface areas of overlap across frameworks before any controls work begins.
- Policy attestation tracking: Distribute policies through a centralized employee portal and track attestations and exceptions with automated follow-up reminders.
- Shared evidence framework: Map controls and evidence tasks once, then automatically apply that work across 50+ overlapping compliance frameworks.
- Real-time risk dashboards: Monitor your compliance and risk posture through dynamic dashboards that update continuously as new data and incidents come in.
OneTrust Integrations
OneTrust offers 50+ integrations including Workday, Zendesk, Snowflake, Salesforce, Box, Power BI, Okta, Slack, Tableau, and Twilio. An API is available for custom integrations.
Pros and Cons
Pros:
- Modular setup lets you scale gradually
- Regulatory guidance across 300+ jurisdictions
- Pre-mapped controls across 50+ frameworks
Cons:
- Some modules feel disconnected from others
- Initial setup is complex and time-consuming

Diligent is a practitioner-led compliance program that pairs in-house expert guidance with Diligent's GRC platform to support effective compliance, program assessments, regulatory risk analysis, policy modernization, and multi-year compliance roadmapping.
Who Is Diligent Best For?
Diligent is a strong fit for enterprise compliance teams that need outside expert counsel alongside their internal GRC program, particularly during regulatory change or program buildouts.
Why I Picked Diligent
I picked Diligent as one of the best because no other tool on this list pairs in-house compliance practitioners directly with a GRC platform the way Diligent does. Its CCEPA methodology benchmarks your program against DOJ, UK, and ISO standards, then produces a prioritized, multi-year roadmap. I also use it to configure reporting dashboards and monitoring frameworks directly within the platform, so strategic guidance and day-to-day compliance execution stay connected.
Diligent Key Features
- Speak-up systems: Design and configure internal reporting programs and investigation protocols for employee-reported compliance concerns.
- Third-party risk management: Build vendor risk assessment frameworks to identify and monitor supply chain compliance exposure.
- Code and policy modernization: Review, draft, and manage the full lifecycle of your compliance policy framework.
- Board reporting: Develop executive communication strategies and define effectiveness metrics for compliance program reporting.
Diligent Integrations
The Diligent One Platform integrates with 100+ third-party systems, including Salesforce, SAP, Oracle, and Microsoft. It also integrates with ServiceNow, Jira, GitHub, Qualys, and major BI platforms. An API is available to automate interactions with the platform, build reporting, and integrate with other systems.
Pros and Cons
Pros:
- Maps programs to DOJ and ISO benchmarks
- Tracks regulatory changes across 130+ countries
- Practitioner-led advisory with in-house compliance experts
Cons:
- Dashboard access controls lack granular permissions
- Policy Manager feels inconsistent with other modules

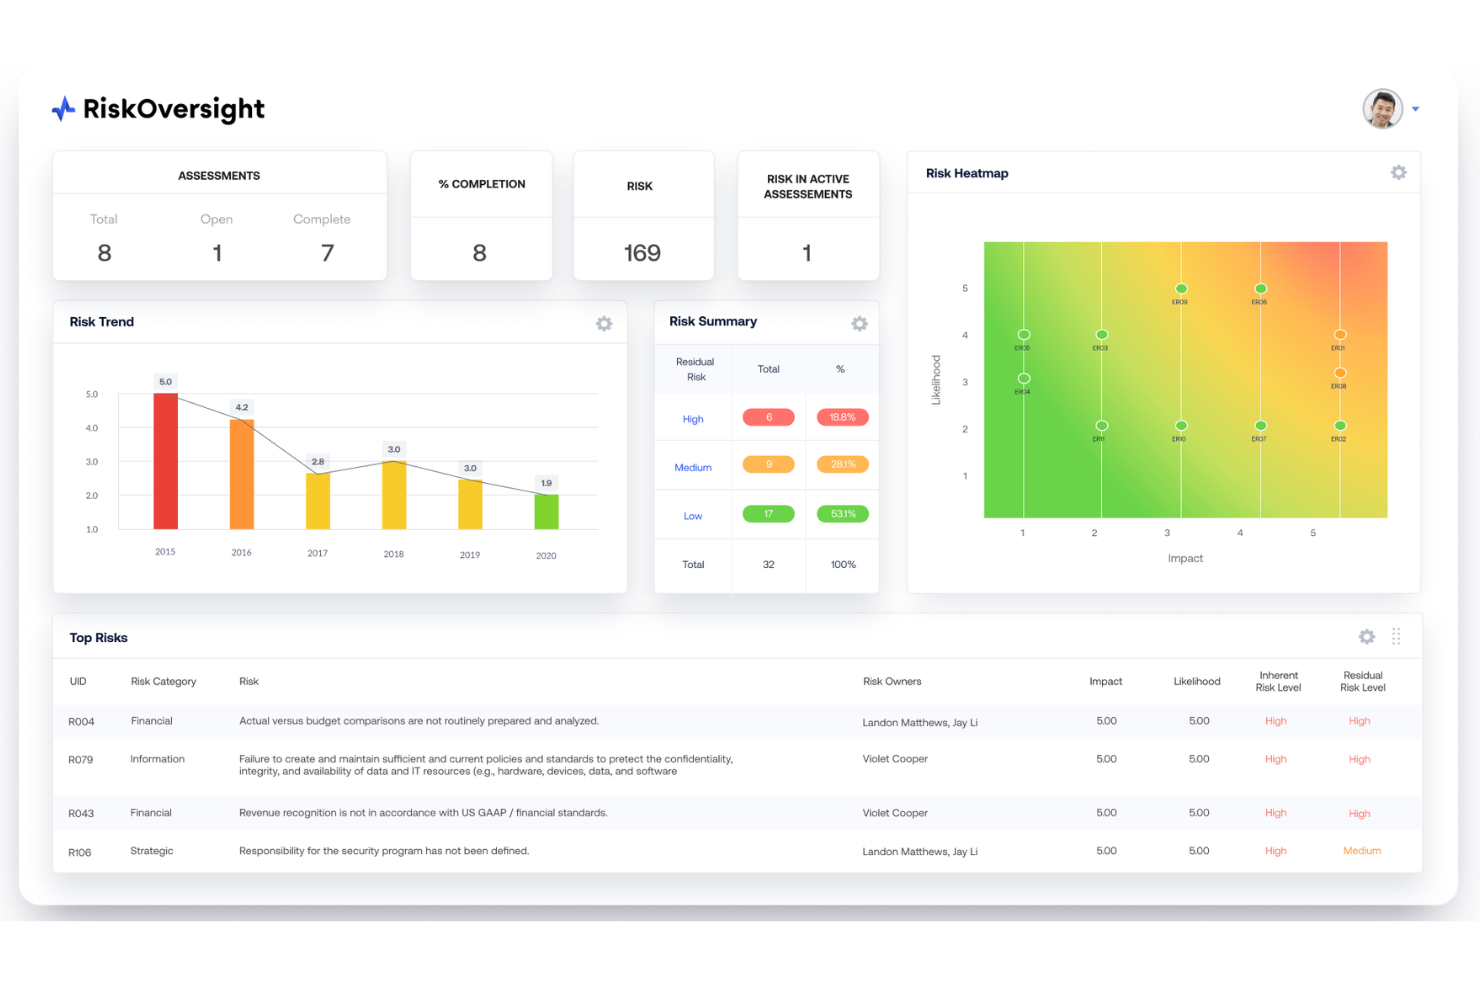
Optro is an AI-powered IT risk and compliance management platform that provides a clear outlook on multi-framework control mapping, continuous monitoring, automated evidence collection, and AI governance across auditable entities.
Who Is Optro Best For?
Optro is a strong fit for IT risk and security teams at large enterprises managing complex, multi-framework cybersecurity compliance programs across multiple auditable entities.
Why I Picked Optro
Optro earns its spot on my shortlist because of how far its AI-driven automation goes inside a compliance workflow. I rely on its AI-powered gap assessments to instantly surface control deficiencies across frameworks like ISO 27001, SOC 2, and NIST CSF, without manual cross-referencing. Optro's automated evidence collection then ties directly into those gaps, so my team isn't chasing down proof after the fact. The continuous monitoring templates give us a live compliance posture rather than a point-in-time snapshot.
Optro Key Features
- Multi-entity compliance management: Manage separate compliance programs for each auditable entity within a single platform, with distinct scopes per entity.
- Control self-assessments: Run structured self-assessments against mapped controls to verify effectiveness across active compliance frameworks.
- Risk and compliance bridging: Connect policies, issues, and exceptions directly to cyber risk data to support risk-driven decision-making.
- AI governance module: Map and track compliance against emerging AI frameworks to manage responsible AI adoption across your organization.
Optro Integrations
Optro offers integrations with Jira, ServiceNow, Azure DevOps, Microsoft Teams, Slack, Google Drive, Microsoft Office, Oracle NetSuite, Workday, Paylocity, and more. An API is available for custom integrations.
Pros and Cons
Pros:
- Shared evidence eliminates redundant collection work
- AI suggests audit procedures and staffing
- Maps controls across multiple frameworks simultaneously
Cons:
- Reporting capabilities lack depth and flexibility
- Creating custom ad hoc audits feels limited
Diğer Uyumluluk Takvimi Yazılımları
Kısa listeme girmeyen ancak yine de göz atmaya değer bazı ek uyumluluk takvimi yazılımı seçenekleri şunlardır:
- NAVEX
For essential regulatory controls coverage
- SAI360
For global regulatory requirement tracking
- LexComply
For automated legal entity management
- Archer
For centralizing policy and risk tasks
- IBM OpenPages
For AI-powered regulatory mapping
- Corporater
For aligning compliance with strategy
- MyComplianceOffice
For conflict of interest monitoring
- Regology (Reggi)
For intelligent global regulation search
- Ncontracts
For financial institution oversight needs
- Star Compliance
For employee conduct tracking


How I Evaluate Compliance Calendar Software
I evaluate every tool on two levels: the core scheduling, tracking, and audit-log functionality it needs to qualify, and what distinguishes it for multi-jurisdiction GRC teams.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. Then, I calculate the tool's total score as a percentage. Each tool needs to achieve a minimum total score of 65% to be considered for inclusion.
- Regulatory deadline tracking: I check whether the calendar supports multi-jurisdiction views with filtering, so teams handling filings across several regulatory bodies aren't toggling between systems.
- Recurring obligation scheduling: I look for recurrence logic that accounts for business days, fiscal periods, and holiday shifts rather than just basic monthly or quarterly repeats.
- Task assignment and ownership: I evaluate whether tasks can be assigned to individuals or teams with status tracking and approval chains that mirror real compliance sign-off workflows.
- Automated notifications and escalations: Multi-channel alerts matter here. I look for tiered reminders and supervisor escalation paths, not just a single email notification.
- Audit trail and reporting: I consider whether the tool logs completions with timestamps and evidence attachments, and whether reports can be exported in formats auditors expect.
- Regulatory content library: Pre-built obligation templates or regulatory feeds save significant setup time. I look at how broad the coverage is and how often content is updated.
Once I have a list of tools that meet this criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
Automated regulatory update feeds are a major differentiator. Some platforms pull amended deadlines directly from regulatory agencies, which saves your team from manually monitoring changes. I also look at configurable alert cadences—tiered reminders at 90, 60, 30, and 7 days out, with escalation to supervisors for overdue items to give teams real breathing room to act before a deadline becomes a crisis. An evidence and document repository matters just as much, since attaching filings and proof of completion directly to calendar events keeps your audit trail intact without chasing files across shared drives.
Beyond Features
Industry specialization matters a lot here. I check whether a vendor pre-loads regulatory content for specific sectors like financial services or healthcare, and how often that content is updated. Implementation support is another factor I weigh—some vendors assign dedicated managers to migrate your existing obligations and historical filings, while others leave that work to your team. I also evaluate integration depth, especially native connections with document management and communication tools your compliance team already uses daily.
Uyumluluk Takvimi Yazılımı Nasıl Seçilir?
Uzun özellik listeleri ve karmaşık fiyatlandırma yapıları içinde kaybolmak kolaydır. Kendinize özgü yazılım seçimi süreciniz üzerinde çalışırken odağınızı korumanıza yardımcı olmak için göz önünde bulundurmanız gereken faktörleri içeren bir kontrol listesi hazırladık:
| Faktör | Dikkate Alınması Gerekenler |
| Ölçeklenebilirlik | Ekip büyüklüğünüz iki katına çıkarsa veya mevzuat kapsamı yeni yetki alanlarına genişlerse yazılım yine de ihtiyaçlarınıza uygun olacak mı? |
| Entegrasyonlar | Ekibinizin güvendiği belge yönetim sistemine, GRC araçlarına ve iletişim platformlarına bağlanabiliyor mu? |
| Özelleştirilebilirlik | Hatırlatıcı sıklıkları, görev iş akışları ve kullanıcı rolleri, kendinize özgü uyumluluk modelinize göre uyarlanabiliyor mu? |
| Kullanım kolaylığı | Uyumluluk, hukuk ve denetim ekiplerindeki kullanıcılar, minimum eğitimle sistemi hızlı bir şekilde öğrenebiliyor mu? |
| Uygulama ve işe alıştırma | Geçiş ne kadar sürecek ve tedarikçinin personeli geçmişe dönük son tarihlerin sisteme yüklenmesine veya uygulamalı eğitim sağlanmasına yardımcı olacak mı? |
| Maliyet | Kullanıcı lisansları, mevzuat içeriği veya bütçenizi etkileyebilecek modül eklentileri için gizli ücretler var mı? |
| Güvenlik önlemleri | Yazılım, kurum içi politikalarınızla uyum sağlamak için gerekli sertifikaları ve esnek veri yerleşimi seçeneklerini sunuyor mu? |
| İç kaynak ihtiyaçları | Ekibinizin kullanıma alındıktan sonra sürekli yönetici veya BT desteğine ihtiyacı olacak mı, yoksa bakım mevcut personelle yönetilebilir mi? |
Uyumluluk Takvimi Yazılımı Nedir?
Uyumluluk takvimi yazılımı, kuruluşların mevzuata ilişkin son tarihleri izlemesine, uyumluluk görevlerini atamasına ve izlemesine ve denetime hazır kayıtları tutmasına yardımcı olan özel bir platformdur. Bu araçlar, bildirim yükümlülüklerini ortak bir takvimde merkezileştirir, hatırlatıcıları otomatikleştirir ve yetki alanları veya mevzuatlar genelinde yinelenen planlamayı destekler. Uyumluluk ekipleri bu araçları hesap verebilirliği artırmak, manuel takibi azaltmak ve denetimler ya da mevzuata ilişkin incelemeler için belgeler hazırlamak amacıyla kullanır.
Özellikler
Uyumluluk takvimi yazılımı seçerken aşağıdaki temel özelliklere dikkat edin:
- Düzenleyici takvim görünümü: Konuya, tüzel kişiye veya yargı bölgesine göre filtrelemeyi destekleyen, yaklaşan tüm bildirim son tarihlerini ve yükümlülükleri okunması kolay, merkezi bir takvimde görüntüler.
- Yinelenen zamanlama motoru: Yıllık, üç aylık veya aylık bildirimler için özel yinelenme kurallarıyla uyumluluk görevlerinin oluşturulmasını otomatikleştirir; tatiller veya mali dönem kesim tarihleri için istisnalar da içerir.
- Görev atamaları ve durum takibi: Görevlerin sorumluluğunu kişilere veya ekiplere atamanıza, ilerlemeyi izlemenize ve uyumluluk yaşam döngüsü boyunca durum değişikliklerini görüntülemenize olanak tanır.
- Otomatik hatırlatıcılar ve eskalasyonlar: Paydaşları güncel tutmak ve son tarihlerin kaçırılmasını önlemek için e-posta veya diğer kanallar üzerinden zamanında uyarılar ve yapılandırılabilir eskalasyonlar gönderir.
- Denetim izi ve kayıt tutma: Denetime kolayca hazırlanmak ve inceleme yapmak için tamamlanan görevlerin, eklenen kanıtların ve kullanıcı işlemlerinin ayrıntılı ve değiştirilemez bir kaydını tutar.
- Düzenleyici içerik kitaplığı: Manuel veri girişini azaltmak ve doğruluğu artırmak için yükümlülük şablonları, yerleşik düzenleyici gereklilikler veya güncel yasalara bağlantılar sağlar.
- Özel raporlama araçları: Kullanıcıların uyumluluk durumunu, tamamlanan işlemleri ve döneme veya kategoriye göre bekleyen öğeleri özetleyen dışa aktarılabilir raporlar oluşturmasına olanak tanır.
- Belge ve kanıt deposu: Destekleyici belgeleri, bildirimleri ve tamamlanma kanıtlarını güvenli ve merkezi erişim için doğrudan her takvim kaydında saklar.
- Birden çok yargı bölgesi desteği: Farklı bölgeler, düzenleyici çerçeveler veya ticari tüzel kişiler genelindeki uyumluluk gerekliliklerinin izlenmesini ve yönetilmesini sağlar.
- Kullanıcı izinleri ve erişim denetimleri: Yöneticilerin gizli uyumluluk verilerini korumak ve onay iş akışlarını yönetmek için rolleri, ayrıcalıkları ve erişim düzeylerini yapılandırmasına olanak tanır.
Faydalar
Uyumluluk takvimi yazılımını uygulamak, ekibiniz ve işletmeniz için çeşitli faydalar sağlar. Yararlanabileceğiniz bazı faydalar şunlardır:
- Son tarihlerin kaçırılma riskinin azalması: Otomatik hatırlatıcılar ve merkezi takip, kritik hiçbir bildirim veya uyumluluk tarihinin gözden kaçmamasına yardımcı olur.
- Gelişmiş hesap verebilirlik: Görev atama özellikleri ve durum takibi, sorumluluğu netleştirerek her yükümlülükten kimin sorumlu olduğunu kolayca görmenizi sağlar.
- Denetime hazırlık: Değiştirilemez kayıtlar ve kanıt depoları, her uyumluluk işlemini ve destekleyici dosyayı belgeleyerek denetim hazırlığını kolaylaştırır.
- Birden çok yargı bölgesinin kolaylaştırılmış yönetimi: Birleştirilmiş takvim görünümleri ve düzenleyici filtreleme, ülkeler veya bölgeler genelindeki gerekliliklerin izlenmesini kolaylaştırır.
- Daha az manuel çaba: Yerleşik düzenleyici içerik kitaplıkları ve otomatik zamanlama, manuel veri girişi ve tekrarlayan yönetim işlerine duyulan ihtiyacı azaltır.
- Yeni ekip üyelerinin daha hızlı işe alıştırılması: Anlaşılır takvimler, iş akışları ve role dayalı izinler, yeni personelin devam eden uyumluluk çalışmalarına hızla uyum sağlamasına olanak tanır.
- Gelişmiş iş birliği: Paylaşılan takvimler ve eskalasyon iş akışları, hukuk, risk ve uyumluluk ekipleri arasındaki ekip çalışmasını ve iletişimi geliştirir.
Maliyetler ve Fiyatlandırma
Uyumluluk takvimi yazılımı seçmek, mevcut çeşitli fiyatlandırma modellerinin ve planların anlaşılmasını gerektirir. Maliyetler özelliklere, ekip büyüklüğüne, eklentilere ve diğer unsurlara göre değişir. Aşağıdaki tabloda yaygın planlar, ortalama fiyatları ve uyumluluk takvimi yazılımı çözümlerinde genellikle bulunan özellikler özetlenmektedir:
Uyumluluk Takvimi Yazılımı İçin Plan Karşılaştırma Tablosu
| Plan Türü | Ortalama Fiyat | Yaygın Özellikler |
| Ücretsiz Plan | $0 | Temel takvim görünümü, sınırlı görev atamaları, manuel hatırlatıcılar ve minimum belge depolama alanı. |
| Kişisel Plan | $10-$25/kullanıcı/ay | Tek kullanıcı erişimi, standart takvim özellikleri, otomatik e-posta hatırlatıcıları, temel raporlama ve dosya ekleri. |
| İşletme Planı | $30-$60/kullanıcı/ay | Çok kullanıcılı destek, ekip atamaları, yinelenen zamanlama, denetim kayıtları, özelleştirilebilir uyarılar ve düzenleyici kitaplık. |
| Kurumsal Plan | $70-$150/kullanıcı/ay | Gelişmiş entegrasyonlar, SSO, role dayalı erişim denetimleri, özel destek, sektöre özgü içerik ve gelişmiş raporlama. |
Uyum Takvimi Yazılımı SSS
Uyum takvimi yazılımı hakkında sık sorulan bazı soruların yanıtları aşağıda yer almaktadır:
Uyum takvimi yazılımı platformları değişen son tarihleri nasıl yönetir?
Çoğu platform, asıl yükümlülüğü gözden kaçırmadan görevleri düzenlemenize veya yeniden planlamanıza ve son tarih değişikliklerini denetim izine kaydetmenize olanak tanır. Güncellemeler yaptığınızda yeni hatırlatmalar gönderen araçları tercih edin; böylece ekibiniz eşgüdüm içinde kalır.
Uyum takvimi yazılımı uluslararası düzenleyici gerekliliklere yardımcı olabilir mi?
Evet, bazı çözümler birden fazla yargı alanını izlemeyi destekler. Son tarihleri bölgeye veya düzenleyici kuruma göre filtrelemenize olanak tanırlar; bu, çeşitli ülkelerde veya düzenleyici ortamlarda bildirimleri yönetiyorsanız faydalıdır.
Entegrasyon desteği açısından nelere dikkat etmeliyim?
Yazılımın belge yönetimi, GRC ve iletişim araçlarınıza yerel bağlantılar sunup sunmadığını kontrol edin. Güçlü API seçenekleri, güncellemeleri otomatikleştirmenize ve verileri mevcut sistemlerinizle senkronize etmenize olanak tanır; bu da manuel veri girişini ve olası hataları azaltır.
Bu araçlar denetime hazır belgeler sunuyor mu?
Evet, çoğu uyum takvimi yazılımı platformu zaman damgaları ve tamamlanma kanıtı ekleri içeren denetim izleri sunar. Bu özellik, kimin neyi, ne zaman ve hangi destekleyici kanıtla tamamladığını tam olarak göstererek harici denetimlerin veya düzenleyici kurum taleplerinin verimli bir şekilde karşılanmasını destekler.
Uyum ekibimi sisteme dahil etmek ne kadar zor?
Uygulama süreci değişiklik gösterir. Bazı sağlayıcılar veri aktarımı ve eğitim desteği sunarken, diğerleri yükümlülükleri manuel olarak girmenizi gerektirir. Kurulum süresinin devam eden uyum faaliyetlerini aksatıp aksatmayacağını veya rehberli bir sisteme dahil olma sürecinin mevcut olup olmadığını öğrenmeniz gerekir.
Uyum verilerim bu platformlarda güvende mi?
Çoğu sağlayıcı SOC 2 sertifikasyonu, şifreleme ve ayrıntılı kullanıcı izinleri gibi güçlü güvenlik uygulamalarını izler. Yine de platformun güvenlik sertifikalarının ve veri yerleşimi seçeneklerinin kurum içi uyum gerekliliklerinizle uyumlu olup olmadığını mutlaka kontrol edin.